

Leads technology risk, application security, AI governance, and compliance assessments across applications, cloud services, platforms, third parties, and AI solutions. Defines assessment scope, evaluates controls and residual risk, documents findings, oversees remediation, supports incidents, and provides management reporting. The role also contributes to security policies, assessment methodologies, DevSecOps governance, secure software development, AI risk management, and continuous improvement while collaborating with technical, legal, privacy, compliance, and business stakeholders.
ZS is a place where passion changes lives. As a management consulting and technology firm focused on improving life and how we live it, we transform ideas into impact by bringing together data, science, technology and human ingenuity to deliver better outcomes for all. Here you'll work side-by-side with a powerful collective of thinkers and experts shaping life-changing solutions for patients, caregivers and consumers, worldwide. ZSers drive impact by bringing a client-first mentality to each and every engagement. We partner collaboratively with our clients to develop custom solutions and technology products that create value and deliver company results across critical areas of their business. Bring your curiosity for learning, bold ideas, courage and passion to drive life-changing impact to ZS.
Lead - Governance, Risk & Compliance
ZS is looking for a skilled and driven Lead- Governance, Risk & Compliance to join its Governance, Risk, and Compliance team. The consultant will serve as a hands-on Technology Risk Assessment subject-matter expert for applications, products, platforms, AI solutions, tools, cloud services, third-party technologies, and emerging technologies.
Independently lead and deliver risk-based assessments covering Application Security Governance, AI Risk Assessment, project risk, and material changes for internal, client-facing, cloud-hosted, client-hosted, third-party, and AI-enabled solutions.
What You'll Bring:
How you'll grow:
Perks & Benefits:
At ZS, your growth matters. We offer a comprehensive total rewards package that supports your health and well-being, financial future, time away, and professional development. With robust skills-building programs, multiple career progression paths, internal mobility, and a deeply collaborative culture, you'll have the opportunity to do meaningful work, expand your capabilities, and thrive as part of a global community. For details on total rewards in India , visit ZS India office locations | Where we work | ZS .
Hybrid working model:
We are committed to giving our employees a flexible and connected way of working. A flexible and connected ZS allows us to combine work from home and on-site presence at clients/ZS offices for the majority of our week. The magic of ZS culture and innovation thrives in both planned and spontaneous face-to-face connections.
Travel:
Travel is a requirement at ZS for client facing ZSers; business needs of your project and client are the priority. While some projects may be local, all client-facing ZSers should be prepared to travel as needed. Travel provides opportunities to strengthen client relationships, gain diverse experiences, and enhance professional growth by working in different environments and cultures.
Considering applying?
At ZS, we honor the visible and invisible elements of our identities, personal experiences, and belief systems-the ones that comprise us as individuals, shape who we are, and make us unique. We believe your personal interests, identities, and desire to learn are integral to your success here. We are committed to building a team that reflects a broad variety of backgrounds, perspectives, and experiences. Learn more about our inclusion and belonging efforts and the networks ZS supports to assist our ZSers in cultivating community spaces and obtaining the resources they need to thrive.
If you're eager to grow, contribute, and bring your unique self to our work, we encourage you to apply.
ZS is an equal opportunity employer and is committed to providing equal employment and advancement opportunities without regard to any class protected by applicable law.
To complete your application:
Candidates must possess or be able to obtain work authorization for their intended country of employment. An on-line application, including a full set of transcripts (official or unofficial), is required to be considered.
NO AGENCY CALLS, PLEASE.
Find Out More At:
www.zs.com
Lead - Governance, Risk & Compliance
ZS is looking for a skilled and driven Lead- Governance, Risk & Compliance to join its Governance, Risk, and Compliance team. The consultant will serve as a hands-on Technology Risk Assessment subject-matter expert for applications, products, platforms, AI solutions, tools, cloud services, third-party technologies, and emerging technologies.
Independently lead and deliver risk-based assessments covering Application Security Governance, AI Risk Assessment, project risk, and material changes for internal, client-facing, cloud-hosted, client-hosted, third-party, and AI-enabled solutions.
- Independently lead and deliver risk-based assessments covering Application Security Governance, AI Risk Assessment, project risk, and material changes for internal, client-facing, cloud-hosted, client-hosted, third-party, and AI-enabled solutions.
- Determine assessment scope, risk tier, and applicable security and governance requirements based on business criticality, data classification, external exposure, hosting model, technology stack, user population, regulatory and contractual obligations, AI usage, third-party dependencies, and the nature and magnitude of change.
- Develop a comprehensive understanding of the solution and its risk context, including business functionality, user journeys, architecture, data flows, trust boundaries, integrations, deployment models, privileged and administrative access, and operational dependencies to identify credible risk scenarios.
- Perform risk assessments throughout the solution lifecycle, including ideation, architecture and design, development, testing, release, production operations, material changes, migrations, and decommissioning.
- Participate in architecture and design reviews, governance stage gates, release-readiness, and production-readiness reviews, identifying security and technology risks and providing documented, risk-based recommendations.
- Evaluate inherent risk, control design and operating effectiveness, residual risk, compensating controls, remediation plans, risk exceptions, and closure evidence in accordance with the approved risk assessment methodology.
- Lead assessment and risk-review discussions with cross-functional stakeholders, including product owners, architects, engineers, developers, data scientists, Security, Privacy, Legal, Compliance, Procurement, and Operations teams.
- Prepare clear, consistent, and defensible risk assessment reports documenting assessment scope, assumptions, system context, evidence reviewed, identified risk scenarios, findings, risk ratings, residual risks, remediation actions, dependencies, and approval or risk-treatment recommendations.
- Track and oversee remediation of high and critical risk findings, including accountable owners, target completion dates, interim or compensating safeguards, escalation, risk acceptance, and validation of evidence prior to closure.
- Support material security incidents, risk escalations, and post-incident reviews by identifying root causes, recurring risk themes and control weaknesses, and recommending improvements to application security and AI risk governance.
- Develop management and governance reporting covering assessment coverage, significant findings, overdue remediation actions, risk exceptions, recurring issues, risk trends, and remediation status to support informed risk decisions.
- Contribute to the continuous improvement of the risk and governance program, including policies, standards, procedures, control libraries, evidence requirements, assessment methodologies and playbooks, training, automation, metrics, and reporting.
- Monitor changes in applicable security, technology, AI, privacy, and regulatory requirements, and support their incorporation into assessment criteria, control requirements, and risk methodologies, including relevant industry frameworks such as ISO/IEC 27001, NIST CSF, NIST AI RMF, and ISO/IEC 42001.
- Experience in performing risk-based Application Security Assessments to identify, evaluate, and manage security risks throughout the application lifecycle, covering architecture review, threat modelling, SAST, DAST, API security testing, SCA, secrets management, penetration testing, CI/CD and IaC security, risk treatment, remediation tracking, and closure validation.
- Experience in assessing application security risks across modern architectures, including microservices, APIs, event-driven systems, containers, Kubernetes, serverless computing, SaaS, PaaS, IaaS, mobile applications, data and analytics platforms, and low-code/no-code solutions.
- Knowledge and experience in evaluating the design and effectiveness of application security controls, including identity and access management, encryption and key management, logging and monitoring, vulnerability management, environment segregation, third-party integrations, incident response, availability, backup and recovery, resilience, and secure decommissioning.
- Experience in reviewing and validating technical evidence to support risk-based assessment conclusions, including architecture and data-flow diagrams, API specifications, threat models, cloud configurations, CI/CD pipelines, security test and vulnerability reports, deployment workflows, operational records, and control demonstrations.
- ISO/IEC 27001 and 27005, ISO 31000, NIST Cybersecurity Framework, NIST SP 800-53/30, NIST Secure Software Development Framework (SP 800-218), SOC 2, CIS Controls and Cloud Security Alliance guidance, including the Cloud Controls Matrix.
- OWASP Top 10, Application Security Verification Standard, API Security Top 10, Software Assurance Maturity Model, OWASP guidance for LLM applications.
- NIST AI Risk Management Framework, ISO/IEC 42001, ISO/IEC 23894, AIUC-1, responsible AI principles and applicable AI regulatory expectations, including the EU AI Act where relevant.
What You'll Bring:
- Bachelor's degree in Computer Science, Information Technology, Cybersecurity, Engineering, Information Systems or a related discipline.
- Minimum of 6+ years of professional experience in technology risk, Application security assessment, Cybersecurity assurance, security architecture, IT Audit, AI assessment & governance, DevSecOps governance - with significant experience at a Big 4, Big 3.
- Demonstrated track record of leading and executing technical security audits - hands-on experience conducting walkthroughs, reviewing evidence, and making independent control assessments
- Strong technical foundation across SDLC governance, CI/CD pipeline security, cloud security controls, access and identity management, application security, and secrets management
- Demonstrated experience independently scoping, conducting, documenting and concluding complex application or technology risk assessments.
- Experience reviewing the work of other assessors and challenging scope, evidence, control conclusions, findings, ratings, remediation and closure decisions.
- Ability to distinguish control design effectiveness from operating effectiveness and determine whether evidence is complete, current, relevant, reliable and sufficient.
- Strong analytical, facilitation, stakeholder-management, technical-writing and executive-communication skills, with the ability to exercise independent judgement and manage concurrent priorities.
- Mandatory certifications - CEH, ISO 27001 Lead auditor, ISO/IEC 42001 Lead Auditor.
- Fluency in English
- Client-first mentality
- Intense work ethic
- Collaborative spirit and problem-solving approach
How you'll grow:
- Cross-functional skills development & custom learning pathways
- Milestone training programs aligned to career progression opportunities
- Internal mobility paths that empower growth via s-curves, individual contribution and role expansions
Perks & Benefits:
At ZS, your growth matters. We offer a comprehensive total rewards package that supports your health and well-being, financial future, time away, and professional development. With robust skills-building programs, multiple career progression paths, internal mobility, and a deeply collaborative culture, you'll have the opportunity to do meaningful work, expand your capabilities, and thrive as part of a global community. For details on total rewards in India , visit ZS India office locations | Where we work | ZS .
Hybrid working model:
We are committed to giving our employees a flexible and connected way of working. A flexible and connected ZS allows us to combine work from home and on-site presence at clients/ZS offices for the majority of our week. The magic of ZS culture and innovation thrives in both planned and spontaneous face-to-face connections.
Travel:
Travel is a requirement at ZS for client facing ZSers; business needs of your project and client are the priority. While some projects may be local, all client-facing ZSers should be prepared to travel as needed. Travel provides opportunities to strengthen client relationships, gain diverse experiences, and enhance professional growth by working in different environments and cultures.
Considering applying?
At ZS, we honor the visible and invisible elements of our identities, personal experiences, and belief systems-the ones that comprise us as individuals, shape who we are, and make us unique. We believe your personal interests, identities, and desire to learn are integral to your success here. We are committed to building a team that reflects a broad variety of backgrounds, perspectives, and experiences. Learn more about our inclusion and belonging efforts and the networks ZS supports to assist our ZSers in cultivating community spaces and obtaining the resources they need to thrive.
If you're eager to grow, contribute, and bring your unique self to our work, we encourage you to apply.
ZS is an equal opportunity employer and is committed to providing equal employment and advancement opportunities without regard to any class protected by applicable law.
To complete your application:
Candidates must possess or be able to obtain work authorization for their intended country of employment. An on-line application, including a full set of transcripts (official or unofficial), is required to be considered.
NO AGENCY CALLS, PLEASE.
Find Out More At:
www.zs.com
ZS Pune, Mahārāshtra, IND Office
ZS Pune (International Tech Park) Office
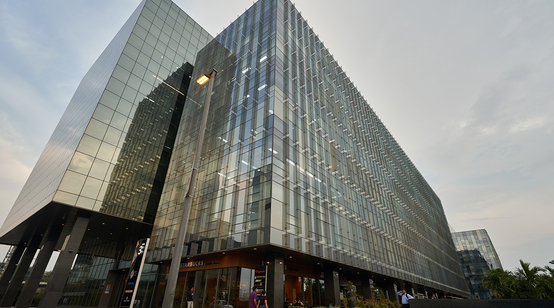




International Tech Park, Panchshil Towers Tower-C, ITPP, Vitthal Nagar, Kharadi, Pune, Maharashtra, India, 412207
ZS Pune, Mahārāshtra, IND Office
ZS Pune (World Trade Center) Office


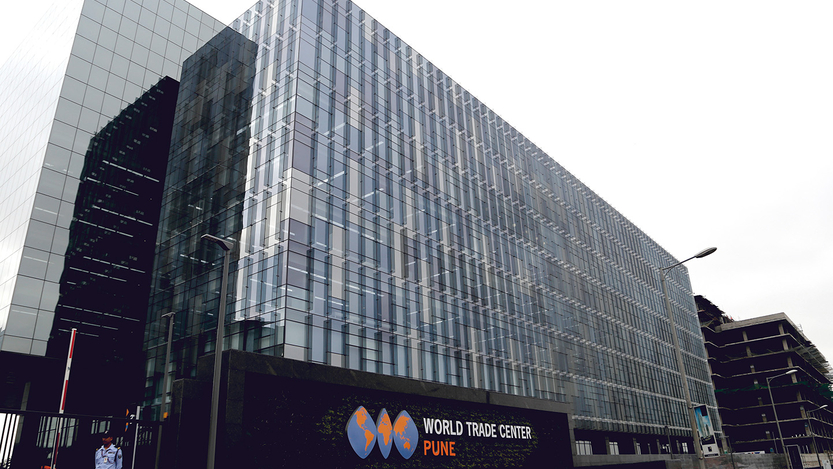


ZS moved to its state-of-the-art World Trade Center office in 2016. Pune is a leading hub for tech talent in India.
Similar Jobs at ZS
Artificial Intelligence • Healthtech • Professional Services • Analytics • Consulting
Coordinates IT and cloud infrastructure projects from planning through completion. Responsibilities include managing project trackers, schedules, budgets, risks, milestones, vendors, onboarding and offboarding, stakeholder communications, leadership meetings, and process improvements. The role serves as a liaison between IT, vendors, and end users while facilitating cross-functional collaboration and ensuring timely delivery.
Top Skills:
AgileCloud InfrastructureExcelMicrosoft PowerpointScrum
Artificial Intelligence • Healthtech • Professional Services • Analytics • Consulting
Develop and optimize Databricks ETL/ELT pipelines using PySpark, SQL, Delta Lake, and Python. Translate client business problems into technical designs, lead project modules, manage delivery tasks, mentor team members, and collaborate with architects, analysts, and clients. Responsibilities include data governance, documentation, solution architecture, testing, deployment planning, risk mitigation, and delivery of technology solutions in a hybrid, client-facing consulting environment.
Top Skills:
SparkData WarehousingDatabricksDelta LakePysparkPythonRdbmsSQL
Artificial Intelligence • Healthtech • Professional Services • Analytics • Consulting
Manages client invoicing, purchase orders, billing compliance, and financial reporting. Responsibilities include creating and sending invoices, tracking purchase orders, processing billing instructions, maintaining invoice records, resolving invoicing issues, supporting project setup and closeout, and ensuring timely and accurate billing, collection, time, and expense transactions. The role collaborates with project teams, finance partners, colleagues, and clients.
Top Skills:
ExcelMS OfficeOutlookSAPWord
What you need to know about the Pune Tech Scene
Once a far-out concept, AI is now a tangible force reshaping industries and economies worldwide. While its adoption will automate some roles, AI has created more jobs than it has displaced, with an expected 97 million new roles to be created in the coming years. This is especially true in cities like Pune, which is emerging as a hub for companies eager to leverage this technology to develop solutions that simplify and improve lives in sectors such as education, healthcare, finance, e-commerce and more.
